How the Agent Operating System Kernel Exposes Scheduling and Memory as First-Class Syscalls
How kernels enforce scheduling and memory as mandatory resource controls for agents.
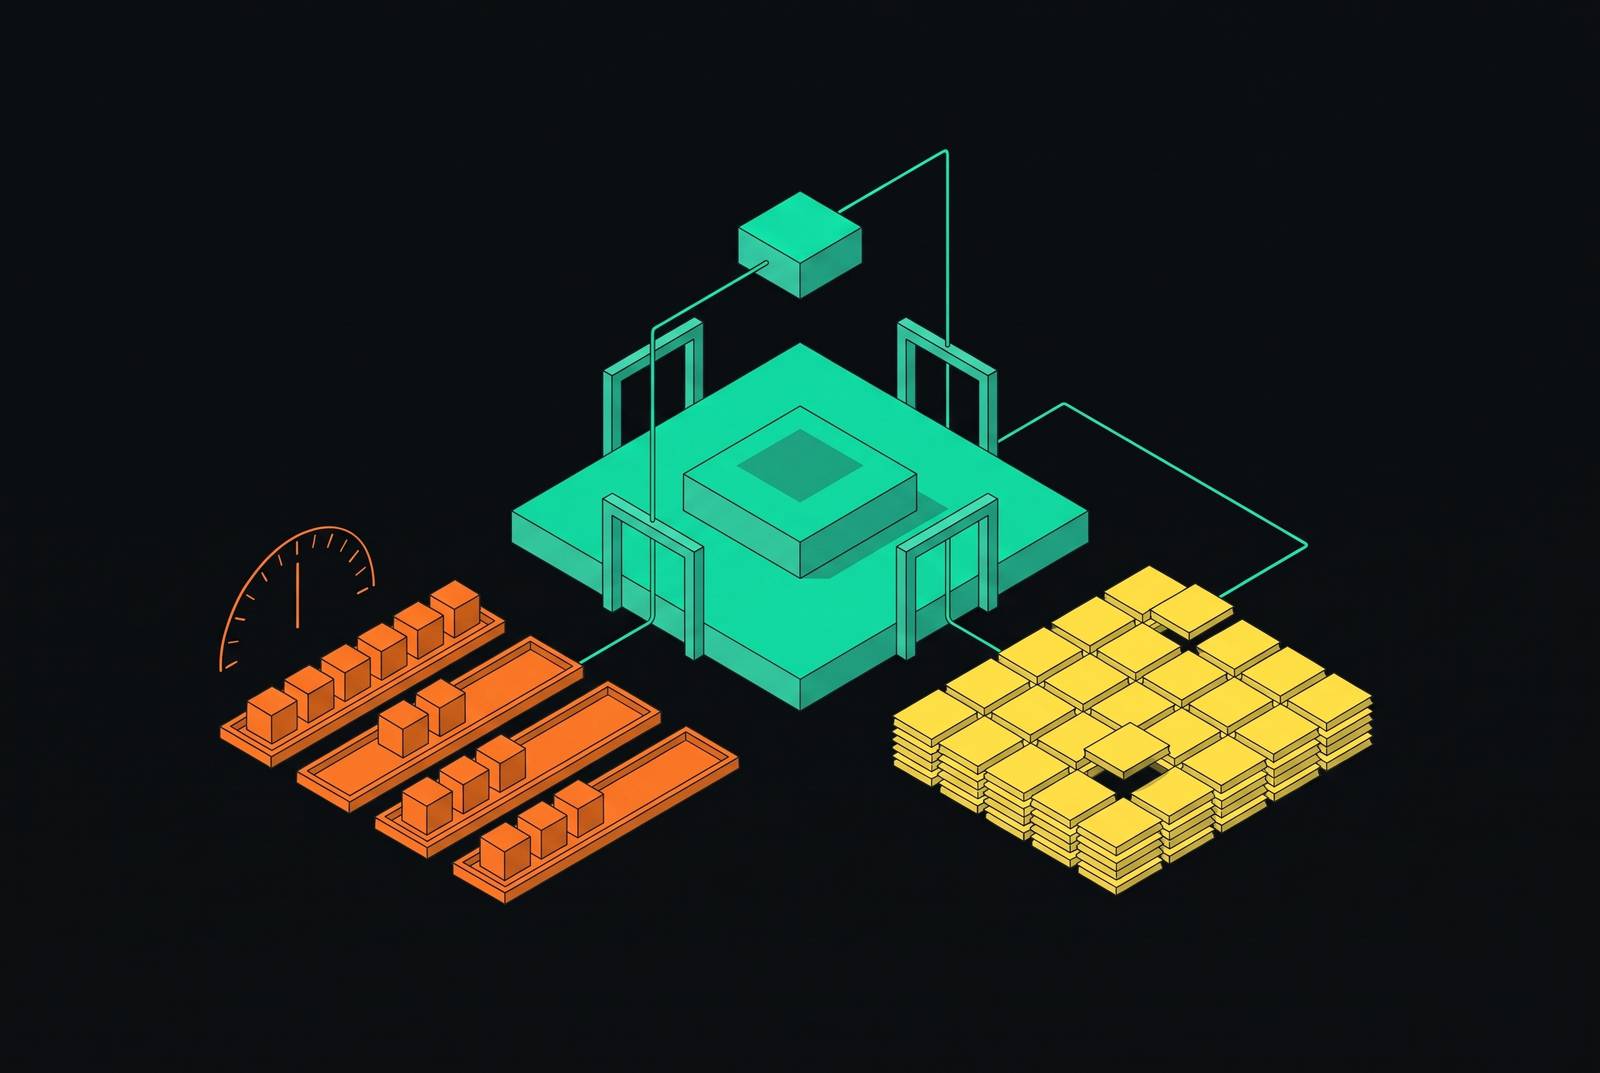
Persistent and scheduled autonomous agents at scale need a runtime that controls when agents run and what they remember between steps. An agent OS kernel earns its name when applications must use its shared syscall interfaces for scheduling and memory. AIOS supplies a concrete kernel design, while Quine, MemOS, Letta, and Cloudflare Agent Memory illuminate different parts of the execution and persistence problem.
Why every serious agent runtime rediscovers the same four primitives
An agent forgets an earlier instruction without warning when its context fills up. Another waits behind a flood of requests. Two agents write to a shared scratchpad and corrupt each other’s state. These failures look different, but they arise from the same mismatch between stateless LLM inference and stateful, long-horizon work. Each inference call starts fresh, but the task needs to carry on across calls, sessions, and concurrent threads.
That mismatch forces runtimes to build a scheduler, a context manager, a memory hierarchy, and a tool router. The context manager handles the finite prompt window, while the memory hierarchy preserves knowledge beyond it. Scheduling handles contention for shared inference resources. When a 30-second research agent and a 200-millisecond triage agent share a naive FIFO queue, the fast agent has to wait behind the slow one. Tool routing and isolation govern shared actions, but when every project implements these controls separately, their guarantees remain local to that project.
What it means to call something a kernel rather than a framework
A kernel is defined by what it enforces. A framework gives agents ways to manage resources, while a kernel stands between agents and resources so that management is not optional. AIOS, by Mei et al. at Rutgers and published at COLM 2025, documents how unrestricted access to LLMs and tools can compromise resource allocation and introduce vulnerabilities. The distinction is therefore not how many useful features a runtime includes. It is whether applications must pass through a controlled boundary to use those features.
What does that boundary buy the application above it? Resource policy no longer depends on every agent behaving correctly or implementing the same conventions. UNIX provides the architectural precedent through well-defined interfaces between processes and the operating system, allowing applications to compose above an enforced contract. The agent-kernel claim applies that arrangement one layer up. Naming resource operations “syscalls” commits the design to mediated access, rather than merely offering helper functions that an agent can bypass.
How AIOS maps agent concerns onto a six-module kernel with explicit syscalls
AIOS makes that commitment concrete by decomposing agent queries into categorized system calls. Its design has six management modules around an LLM Core, making seven modules in the paper’s table. The Agent Scheduler comes first in the running agent’s path because it gates access to limited inference resources. Its interface includes execute_syscall, start, and stop. The LLM Core provides model processing, while the Context Manager governs the context needed for that processing.
The Memory Manager and Storage Manager then separate memory operations from storage operations. The memory interface includes execute_memory_syscall, add_memory, and remove_memory. Those names give agents resource operations to use, so each agent does not have to invent its own persistence conventions. The Tool Manager governs tool use, and the Access Manager governs access. Together, these modules put distinct resource classes behind the kernel boundary, where concurrent agent sessions can be isolated rather than relying on application-level exception handling.
AIOS reports up to 2.1× faster execution when serving agents built with various frameworks. That result shows that interposing a kernel can remove waste from unmanaged contention. It is not a guarantee for every workload. The AIOS SDK supplies the developer-facing APIs above these services, serving much the same role as a standard library above a syscall interface.
Scheduling as a first-class syscall and what the kernel actually arbitrates
Scheduling becomes a system guarantee when agents cannot opt out of it. The kernel can enforce fairness, priority, and resource limits across agents that know nothing about one another. AIOS describes the alternative as agents flooding LLM resources until prompts loaded as tensors exhaust CUDA memory, triggering exceptions and retries that reduce throughput. The shared resource is not just processor time. Context windows, token budgets, and API rate limits also need arbitration across concurrent agent threads.
Quine, by Ke, takes a different starting point by realizing agents as native POSIX processes. Identity becomes a PID, the interface becomes standard streams and exit status, and state lives in process memory, environment variables, and the filesystem. Lifecycle follows fork, exec, and exit. This inherits host scheduling. Operators can use nice, kill, ulimit, and cgroups to control agent processes without framework-specific supervision, although those tools do not express LLM token budgets or context allocation.
XKernel extends scheduling policy across criticality, deadline, efficiency, and cost through a 22-syscall kernel interface specification. Yet agent scheduling also faces a constraint that ordinary CPU scheduling does not. An LLM inference cannot be cleanly suspended mid-token without losing its trajectory, so agent-level scheduling must work at turn boundaries.
Memory as a first-class syscall and why tier placement changes what agents can know
A three-tier memory hierarchy makes the resource problem visible. The bounded context window is hot working memory, always present in the prompt. A warm retrieval store supplies information through similarity search, while cold archival storage preserves longer-term knowledge. MemGPT formalized this hierarchy and called movement between tiers “page faults,” borrowing the vocabulary of kernel memory management. Agents must determine what enters the prompt now and what remains available later.
Those are related decisions, but not identical ones. Context management runs at each inference and determines what fits inside the model’s window. Memory management persists knowledge across sessions and supplies context management with information when needed. Confusing them can produce a system that seems continuous within a conversation but loses that continuity at a session boundary. MemOS, by Li et al., 2025, extends the OS framing by treating parametric memory, activation memory, and explicit plaintext memory as one operating-system-level resource abstraction.
Letta, the productized successor to MemGPT, makes memory management explicit through a stateful runtime. Core memory blocks stay in the prompt, archival memory uses PostgreSQL and pgvector for similarity retrieval, and recall memory is the third part of the three-tier arrangement. The agent decides what to remember, forget, and prioritize through editable memory structures that remain transparent and developer-controlled. Agency does not require unmanaged storage access. An agent can choose memory operations while the runtime does the work that makes those operations persistent.
Cloudflare Agent Memory manages the infrastructure for persistence. Its private beta, announced April 17, 2026, extracts information from agent conversations and makes it available when needed without filling the context window. A 2026 architectural study across thirteen system configurations found that memory control placement between recall and control planes shapes forgetting failures. That finding gives grounds for care in where memory logic goes, but leaves open whether it belongs in kernel or user space. At compaction, the harness must shorten context to fit the model’s limits. Cloudflare’s service preserves knowledge at that boundary instead of letting a shorter prompt become a silent loss of memory.
What grounding agents in POSIX reveals about the limits of the process model for cognition
Quine’s process model inherits more than a scheduler. Hardware-backed address-space separation supplies fault isolation, while kernel-managed pipes provide communication with backpressure. These are real operating-system guarantees. Because agents expose standard streams and exit status, they compose with pipes, scripts, and existing UNIX tools. The runtime does not need framework-specific glue merely to connect one process to another.
Recursive delegation follows from the same design choice. A parent agent spawns the same runtime image with different arguments, making delegation self-instantiation rather than an operation owned by an external orchestrator. The runtime and agent template are the same artifact. This is a serious reduction in machinery. It also sharpens the question of which remaining responsibilities genuinely require an agent-specific runtime instead of another copy of an operating-system service.
Quine identifies task-relative worlds and revisable time as extensions that do not map cleanly onto fork, exec, and exit. The turn-boundary constraint exposes a related visibility problem. A host scheduler’s visibility is limited to executable processes, so it cannot enforce the semantic boundary of an agent’s inference turn itself. These limits explain why a sound execution substrate and a complete cognitive runtime are different architectural goals.
How the syscall interface changes the architecture of the agent stack above it
In the layered model of Agent Surface, Orchestration/Runtime, Memory, and Knowledge, the kernel makes the boundary between orchestration and memory enforceable across frameworks. Multi-agent systems can then decompose requests into subtasks and dispatch work through standardized protocols such as MCP. Those protocols connect tools, data sources, and APIs. They do not replace the scheduling and memory guarantees that keep each dispatched task from negotiating resource access independently.
Resource interfaces that stay the same also make control flow easier to predict. Agentic frameworks in 2026 are moving toward structured state machines with fallback paths rather than relying only on a Thought-Action-Observation loop. That structure needs the system beneath it to enforce state transitions, beyond asking each agent to keep track of its own state. Kernel-mediated lifecycle commands can also serve as inter-agent communication. A parent can use spawn, pause, resume, and terminate to manage children through a common interface, supporting hierarchical decomposition without a separate orchestration layer for lifecycle control.
Agent libOS, described in June 2026, takes the idea toward a library OS. It defines an AgentProcess as the execution unit, gives each process its own working directory, treats humans as sources of authority, and brokers model-facing tools through primitive managers and syscall sessions. Its lineage is an architectural argument. Like the tradeoff explored by 1990s exokernel research, it puts kernel structure into user space so applications can compose it independently of a monolithic kernel. Through the SDK, Quine’s protocol, or a syscall session, builders can use that contract in their programs.
What do builders need to run hundreds of long-running agents reliably?
Production requires scheduling and memory to be observable and controllable together. AIOS provides syscall formalism, Quine provides POSIX grounding, and MemOS provides memory unification. Letta offers a stateful memory runtime, while Cloudflare’s service addresses managed extraction and preservation through compaction. These are distinct capabilities. The descriptions here leave open whether any one option meets all production needs without more work to connect it to other systems.
For builders, the useful comparison starts with operational control. Agents need to be paused, resumed, and terminated without restarting the runtime, with lifecycle commands exposed directly. Persistence must survive session boundaries without developers separately managing compaction, a vector store, and retrieval logic. The interface should also be straightforward to operate. The production target is a single-command start, a CLI that speaks the language of the syscalls, and visibility that does not require custom instrumentation.
Scheduled execution is a separate test from resource fairness. A runtime can arbitrate concurrent requests without providing scheduled or event-triggered wakeups, so proactive agents need both capabilities explicitly. Purpose-built infrastructure is worth the investment when it brings those lifecycle controls together with persistent memory and LLM-specific limits that cgroups and ulimit cannot express. Those include token budgets, context-window allocation, and rate-limit arbitration.